Facing the growing challenges of digital operations, global supply chain collaboration, and evolving cyber threats, information security has become a cornerstone of operational resilience, customer trust, and product and service quality. Guided by the principle that “information security is everyone’s responsibility,” Arcadyan has implemented an Information Security Management System (ISMS) in accordance with ISO 27001 and ISO 27005 standards. The Company has established governance and management mechanisms covering information security governance, risk assessment, incident response, access control, data protection, product security, and employee training to safeguard the confidentiality, integrity, and availability of operational information, customer data, product information, and personal data. Through continual improvement, regular reviews, risk monitoring, and cross-functional collaboration, Arcadyan integrates information security requirements into daily operations, product development, supply chain management, and customer services to strengthen cybersecurity resilience and stakeholder trust.
ISO 27001 Information Security Policy
- Ensure the confidentiality of information related to the business of the Company to prevent breaches or losses of the Company's sensitive information and individual data.
- Ensure the completeness and availability of the Company's business information to perform the operation and various business of the Company correctly.
Information Security Governance Structure
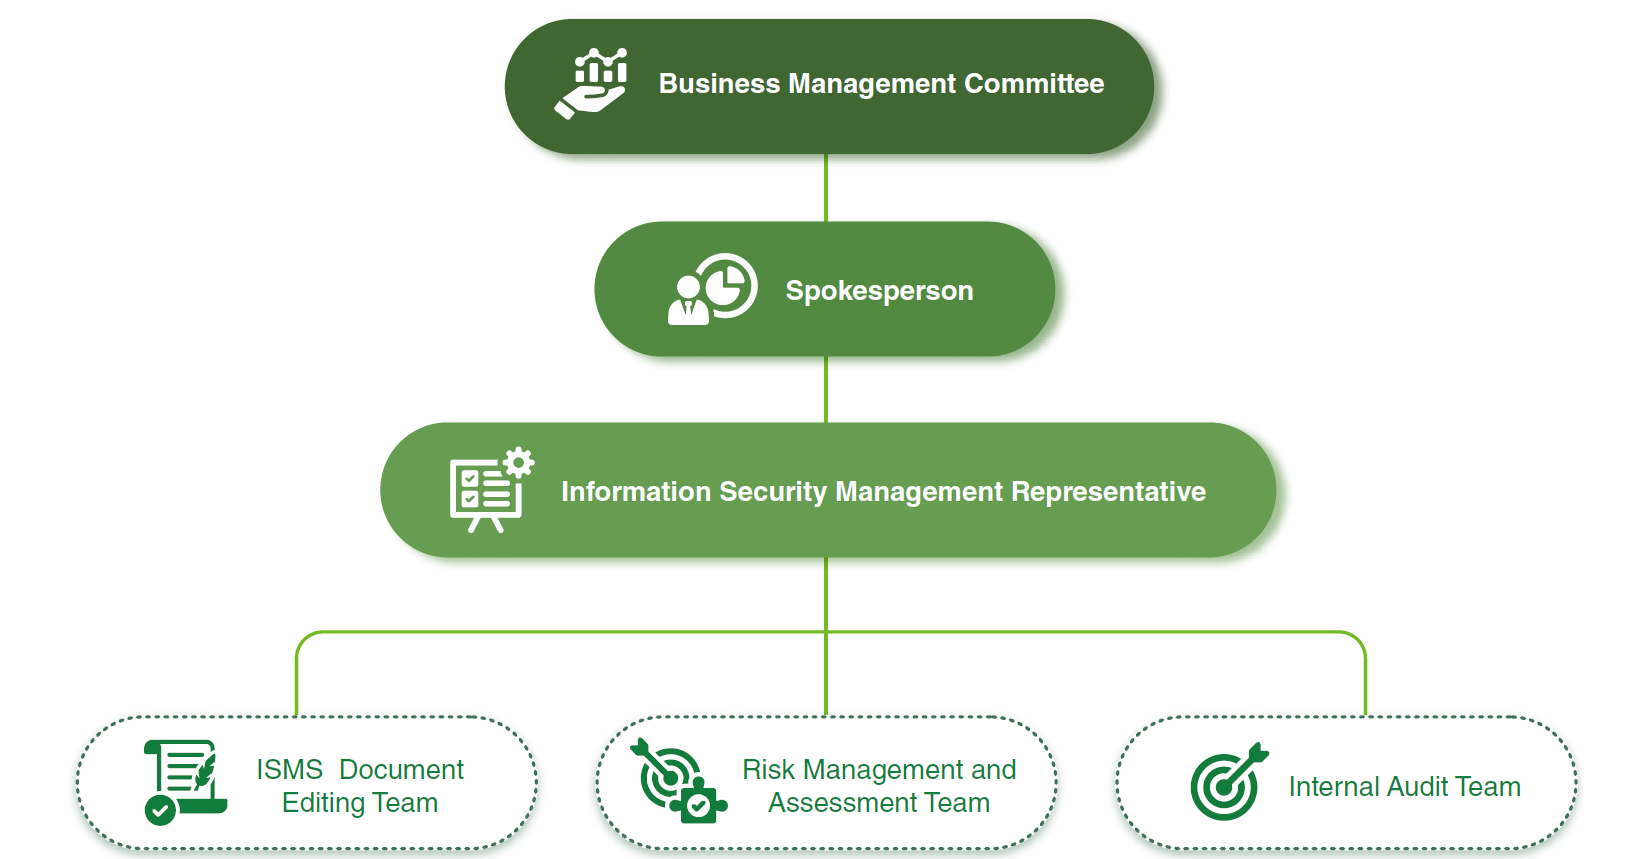
Arcadyan has established the Information Security Management Committee as the central body responsible for overseeing and coordinating information security management. The Committee reviews information security policies, management objectives, risk assessment results, incident response plans, and improvement initiatives, while regularly monitoring the implementation of information security controls to ensure effective execution. Three dedicated working groups, namely the ISMS Document Editing Team, Risk Management and Assessment Team, and Internal Audit Team, support the Committee by managing policy documentation, conducting information asset risk assessments and improvement tracking, and performing internal audits and corrective action reviews. Through clear role allocation and cross-functional collaboration, Arcadyan continuously strengthens its information security governance framework.
At the operational level, dedicated information security teams are responsible for policy implementation, risk assessment, security monitoring, employee training, incident response, and corrective action follow-up. Business units are responsible for implementing data protection, access control, document management, and customer information protection requirements based on their operational needs. Through a top-down governance structure and cross-functional collaboration, Arcadyan integrates information security management into daily operations and decision-making processes. The Company also conducts information security management reviews twice a year to evaluate cybersecurity risks, audit findings, improvement actions, and implementation results across all sites, providing a basis for policy enhancement, resource allocation, and continual improvement.
Information Security Management Mechanism
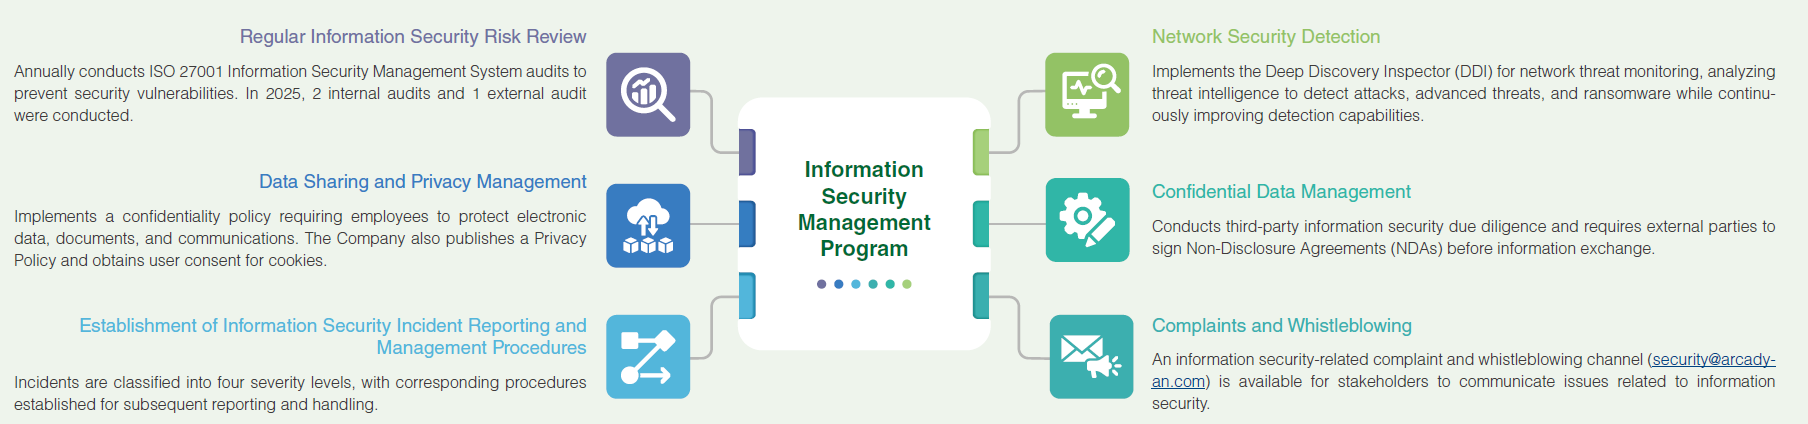
Arcadyan has established a comprehensive information security management system and internal control framework in accordance with the ISO/IEC 27001 standard. Through regular internal and external audits, risk assessments, vulnerability scanning, information asset management, and corrective action tracking, the Company continuously strengthens the confidentiality, integrity, and availability of its information assets while ensuring its security management system remains responsive to an evolving threat landscape. To enhance operational resilience, Arcadyan implements a range of cybersecurity measures, including business impact analysis, disaster recovery drills, account and access management, firewall monitoring, penetration testing, security awareness training, and social engineering exercises to reduce the risks of unauthorized access, data breaches, cyberattacks, and system disruptions. Since 2020, Arcadyan has maintained cybersecurity insurance as part of its risk management strategy, with coverage reaching US$3 million in 2025, reflecting its long-term commitment to information security and proactive risk management.
To mitigate information security risks associated with external ICT service providers, Arcadyan has required relevant suppliers since 2025 to sign the Information Security Cooperation Statement and Obligation Acknowledgment, applicable to contracts, purchase orders, and other forms of written engagement. The agreement defines supplier responsibilities regarding data protection, confidentiality, information transmission, remote access, incident reporting, audit remediation, and third-party outsourcing management. Suppliers are prohibited from accessing, copying, disclosing, or retaining Arcadyan information without authorization and must report any data breach, abnormal operation, or other security incident within two hours of discovery and cooperate with subsequent investigations and corrective actions. In 2025, 23 ICT service providers completed the signing process, strengthening accountability, reducing risks related to data leakage, service interruptions, and regulatory non-compliance, and enhancing overall supply chain cybersecurity resilience.
Information Security Awareness and Training
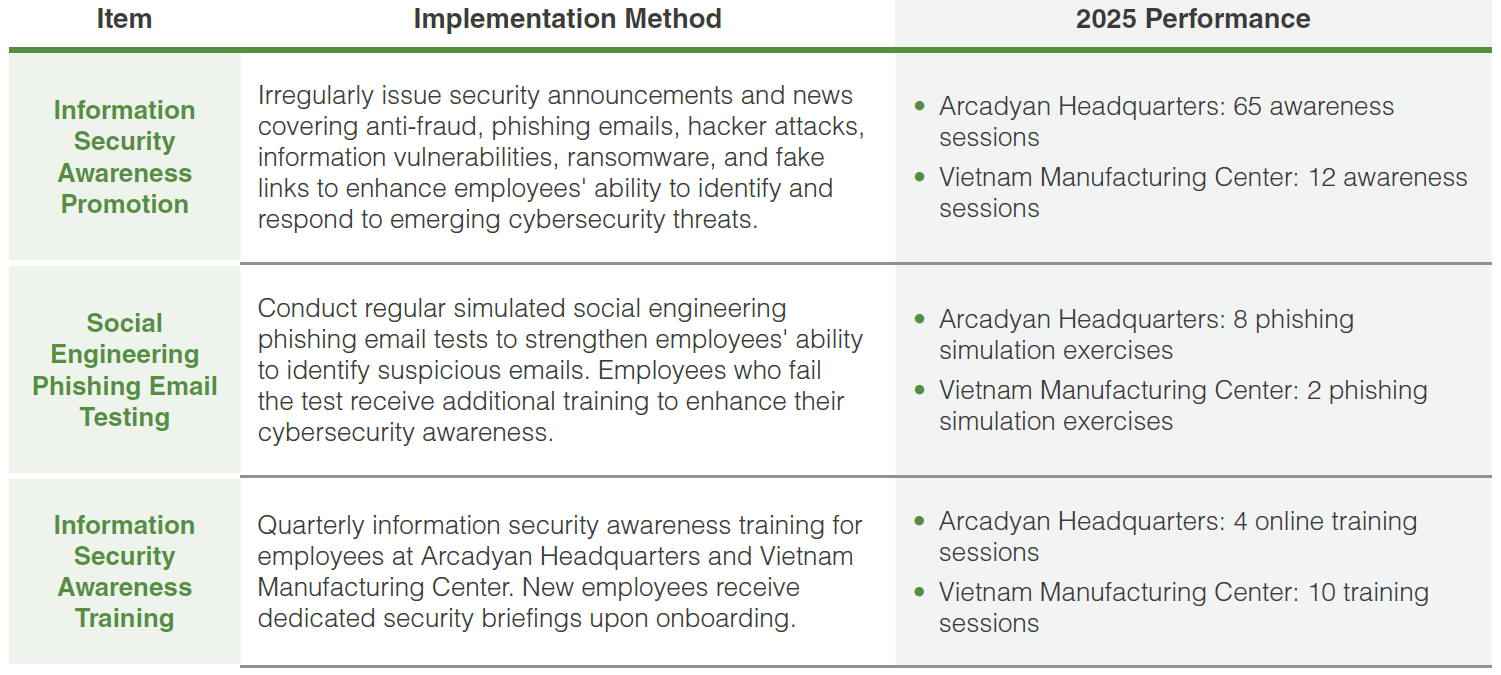
To strengthen information security awareness and promote secure behavior across the organization, Arcadyan implements a variety of cybersecurity awareness and training programs to help employees stay informed of emerging security threats and enhance their ability to identify and respond to potential risks. Through security awareness communications, simulated phishing exercises, and cybersecurity training programs, the Company continuously improves employees’ ability to recognize phishing emails, ransomware, fraudulent links, security vulnerabilities, and other evolving cyber threats, establishing a strong first line of defense against cybersecurity risks.
Data Protection, Privacy Management, and Access Control
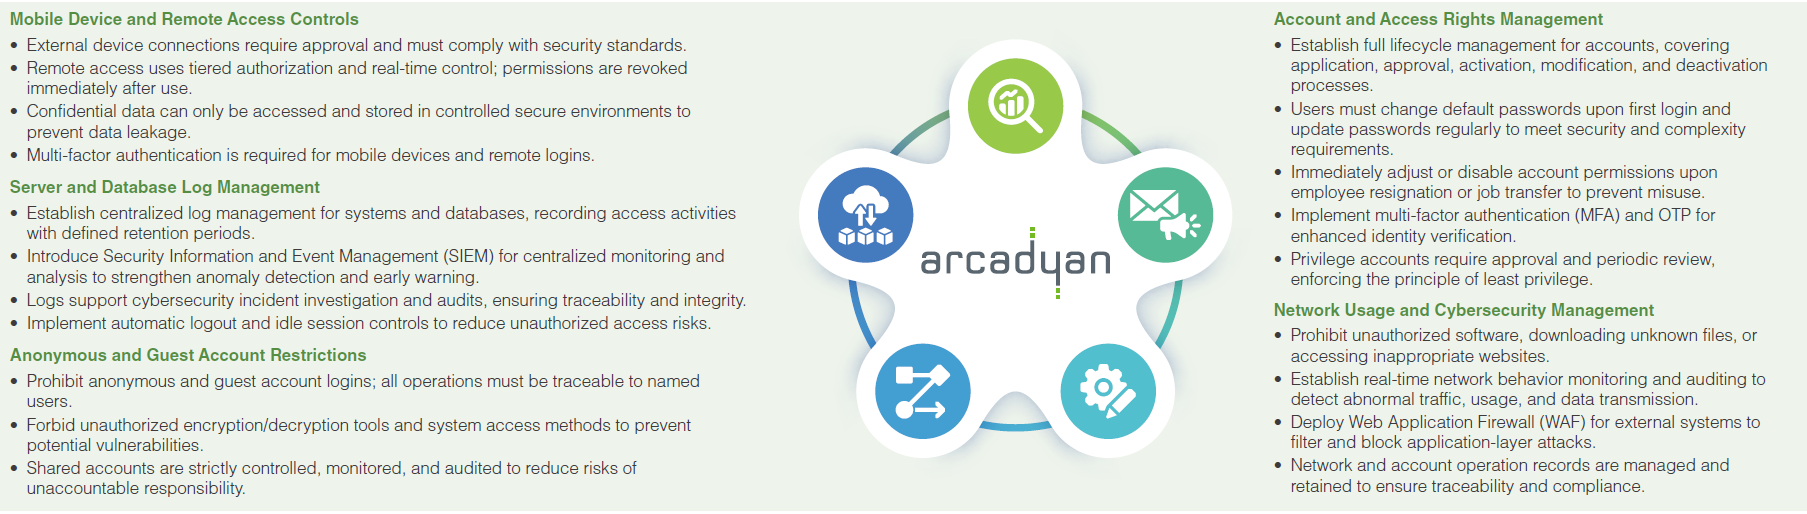
Based on data classification levels and business requirements, Arcadyan has established comprehensive mechanisms for data protection, privacy management, and access control to ensure that operational information, customer documents, product data, and personal information are properly safeguarded throughout their collection, processing, transmission, storage, and disposal. The Company leverages account and access management, multi-factor authentication (MFA), log monitoring, remote access controls, data retention policies, and confidentiality management practices to reduce the risks of unauthorized access, data breaches, and misuse of personal information.
Access Control and Network Security Measures
Customer Data and Confidential Information Protection
Arcadyan has established a comprehensive data governance and protection framework covering the entire data lifecycle, including data retention, use, sharing, and disposal. Through information retention and log management mechanisms, the Company ensures the traceability of system access activities and establishes appropriate retention periods based on regulatory and business requirements to support security investigations and audit activities.
Arcadyan also enforces employee confidentiality obligations by requiring new employees to sign confidentiality commitments and comply with information security policies. Through ongoing training and systematic audit programs, the Company strengthens employee awareness of information protection responsibilities. In addition, Arcadyan publicly discloses its Privacy Policy on its corporate website to promote transparency and ensure the lawful handling of information.
Data and Privacy Protection
To address evolving global data protection requirements and regulatory developments, Arcadyan has established a Privacy Policy in accordance with the General Data Protection Regulation (GDPR) and applicable privacy laws in the regions where it operates. The policy serves as the Company’s highest guiding principle for protecting the personal data of internal and external stakeholders. Arcadyan’s Information Security Department oversees the collection, processing, and retention of personal data to ensure compliance with applicable regulations and internal codes of conduct.
Arcadyan provides dedicated privacy complaint and reporting channels, allowing stakeholders to report potential data misuse or privacy violations through its information security reporting mailbox (security@arcadyan.com). In 2025, the Company received no privacy-related complaints or regulatory penalties and recorded no incidents involving customer privacy infringement or data leakage. Through these measures, Arcadyan continues to reduce risks associated with data breaches and misuse while strengthening information security and operational resilience.